Rising Threat: ClickFix Attacks Target Mac and Windows Users
By Editor • September 14, 2026 • 1 min read
In a concerning trend for cybersecurity, ClickFix attacks are becoming increasingly sophisticated, deceiving both Mac and Windows users into compromising their own devices. These attacks, which exploit users' search for quick tech solutions, have escalated into a widespread threat, with hackers utilizing deceptive ads on platforms like Reddit.
How ClickFix Attacks Work
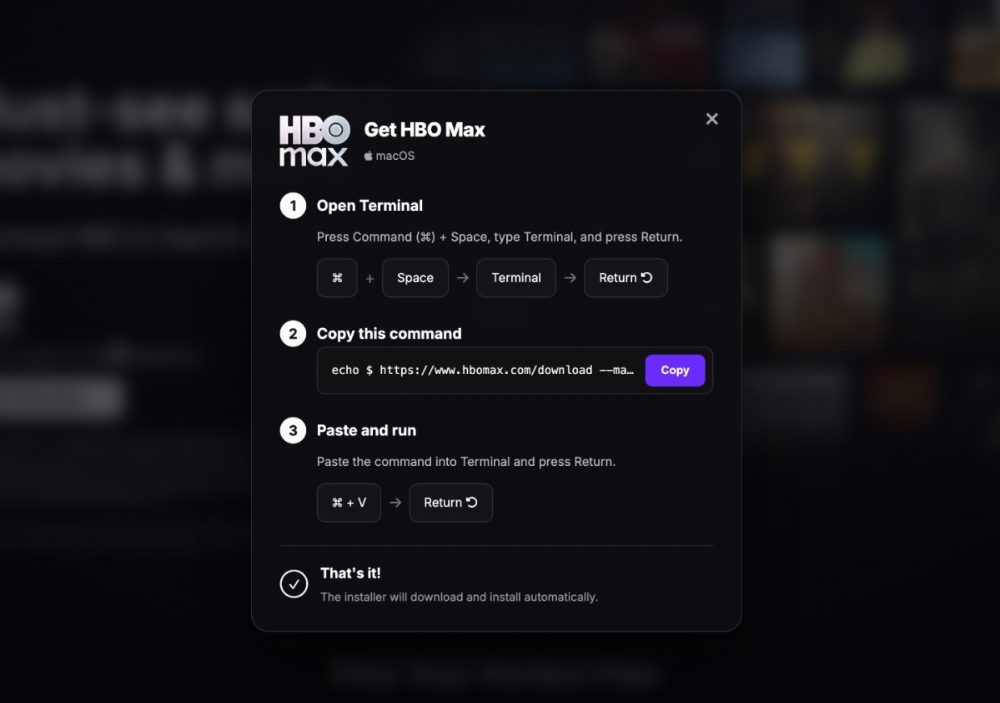
ClickFix attacks typically involve either fake websites or legitimate sites that have been hacked. Users are presented with a message resembling a CAPTCHA or anti-bot verification. When clicked, they are instructed to copy and paste a specific text string into their computer's command prompt or terminal application. This seemingly innocuous action leads to the immediate installation of malware that can steal sensitive information, including passwords and crypto wallet details.
Recent Incidents and Implications
Security experts, including those from Hudson Rock, have identified a recent campaign where hackers posted fake HBO Max ads on Reddit, effectively tricking users into these self-hacking scenarios. Although the number of affected individuals remains unclear, the implications of these attacks are severe. Users, often unaware of the risks of using command-line tools, can unwittingly bypass antivirus protections, making these attacks particularly dangerous.
As organizations like Warner Brothers Discovery and Reddit have yet to comment on these incidents, experts urge users to exercise caution and consider security measures such as blocking command line access in corporate environments or utilizing tools like BlockBlock for Mac users to mitigate risks.
Source: techcrunch.com